 CYBERSECURITY MONTH 2026
Test the human resilience of your teams
For banks, insurers, mutual insurance companies, asset managers and fintechs. Financial fraud targets people first: an urgent wire transfer, a change of bank details, a familiar voice on the phone. BlueSecure trains the roles exposed to these situations, prepares leadership for a crisis and documents every action.
- DORA module in 12 languages
- 8 simulation channels
- Dated, exportable history
Cyber challenges in the financial sector
The human factor is the direct target.
CEO fraud, IBAN fraud, impersonation of an advisor, a call claiming to be from support: payment workflows and back-office roles are targeted first.
The subcontracting chain widens the attack surface.
IT providers, delegated managers, brokers, platforms: the scope to train often goes beyond your own workforce.
The regulator expects evidence.
Awareness programs, leadership training, exercises carried out, results achieved: all of it dated and documented.
Voice deepfakes change the scale.
A reconstructed voice makes an urgent transfer request credible. Dual approval procedures hold when everyone knows they can be fooled.
Train the roles exposed to fraud
Learning paths for roles authorized to make payments
The DORA module sets the framework for everyone, in 12 languages. Sensitive roles then take the Fraud and social engineering, CEO fraud, IBAN fraud and Incident management modules.
Simulations on the channels actually used
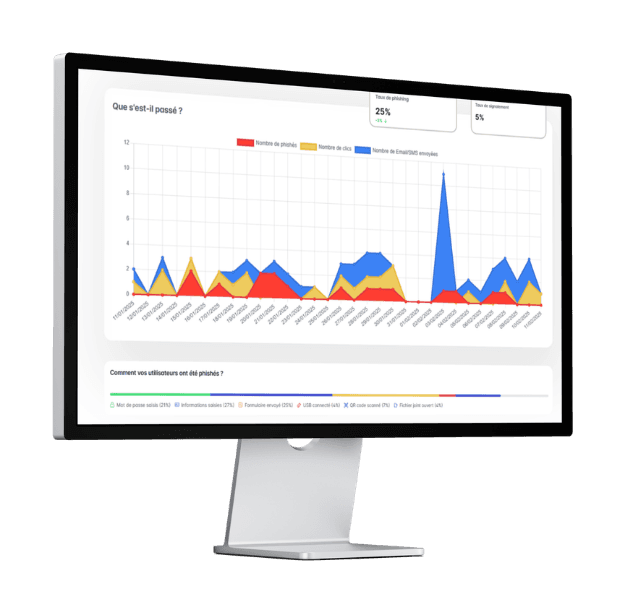
Phishing 360™ covers 8 channels: email, SMS, USB drive, QR code, postal mail, physical intrusion (building breach), phone call (vishing) and deepfake. Urgent transfer and bank detail change scenarios are the most relevant for your sector. Campaigns are individualized and retargeting is based on the risk score.
Report fast
MailWatch™ supports every employee facing a suspicious email: an alert appears in your email environment, and an on-demand analysis button answers in plain language, with an educational debrief. Every report feeds the BlueSecure Risk Index™.
Train leadership for a crisis
BlackOut™, the crisis management escape game from our Game Studio, is played online by all employees. For the executive committee, the BlackOut™ crisis workshop (2 to 4 hours, in person) puts participants through a cyber crisis: qualify the incident, decide under pressure, prepare notification and communication. The executive committee keynote stages a live transfer fraud using the voice of your CFO.
Include your providers
Providers who access your information system can be included in the program, just like your employees. The Supply Chain Attack module covers supply chain risks.
DORA in brief
DORA, in force since January 17, 2025, requires ICT security awareness programs and digital operational resilience training, mandatory for all staff and leadership (Article 13). The management body is responsible for the ICT risk management framework, and its members take specific training on a regular basis (Article 5). ICT service providers are included in these programs where relevant (Articles 13 and 30).
BlueSecure helps implement and document the awareness, training and crisis exercise requirements of DORA.
Prove and manage
Campaign history, individual results, certificates, PDF and Excel exports, API: the evidence builds up as you go. The BlueSecure Risk Index™ tracks the risk level by entity, and Smart Report™ reports share it automatically with leadership and control functions.
For groups made up of several regulated entities, multi-tenant management separates data by entity, delegates administration and consolidates reporting at group level.
Your data stays in France
Platform data is hosted in France by French hosting providers certified ISO 27001, which are not subject to extraterritorial laws such as the US CLOUD Act. If your context requires it, SecNumCloud, dedicated server or on-premise options are available.
- Cas d'OR de la Cybersécurité 2026
- CyberNight 2024 Gold winner
- CyberNight 2025 Coup de Cœur award
They run their program with BlueSecure
Banking and insurance organizations trust us. More than 500 organizations supported · More than 700,000 employees trained · 4.8/5 satisfaction.
Where to start
Phishing 360™
Multichannel simulations based on transfer fraud and impersonation scenarios.
Learning Academy™
The DORA module, the fraud and social engineering modules, incident management.
BlueSecure Risk Index™ and Smart Report™
Dated tracking for your audits.
FAQ
- What does DORA require in terms of cybersecurity awareness?
- ICT security awareness programs and digital operational resilience training, mandatory for all staff and leadership (Article 13). The management body is responsible for the ICT risk management framework (Article 5).
- What evidence should we keep for an audit?
- Dated records: campaigns run, target groups, content delivered, results, certificates. The platform stores them and exports them as PDF and Excel, or through the API.
- Can we simulate CEO fraud by phone?
- Yes. Two channels make this possible: phone calls (vishing) and deepfake, which reproduces a voice using artificial intelligence.
- Can we also train our providers?
- Yes. Providers who access your information system can be included in the scope, just like your employees.
- How do we manage several regulated entities within one group?
- With multi-tenant management: data separated by entity, delegated administrators, reporting for each entity and a consolidated view at group level.
- Where is the data hosted?
- In France, with a French hosting provider certified ISO 27001, outside the scope of the CLOUD Act. A dedicated server, a SecNumCloud option or an installation on your own servers are also possible.
Let's talk about your DORA deadlines
Regulated scope, audits to prepare, groups to cover: we build the program you are missing with you, in the right order.